
← All Apps
Get Public IP Add-on
Splunk Universal Forwarder and Splunk Enterprise
Collects the public IPv4 and IPv6 egress address of every Splunk forwarder and host.
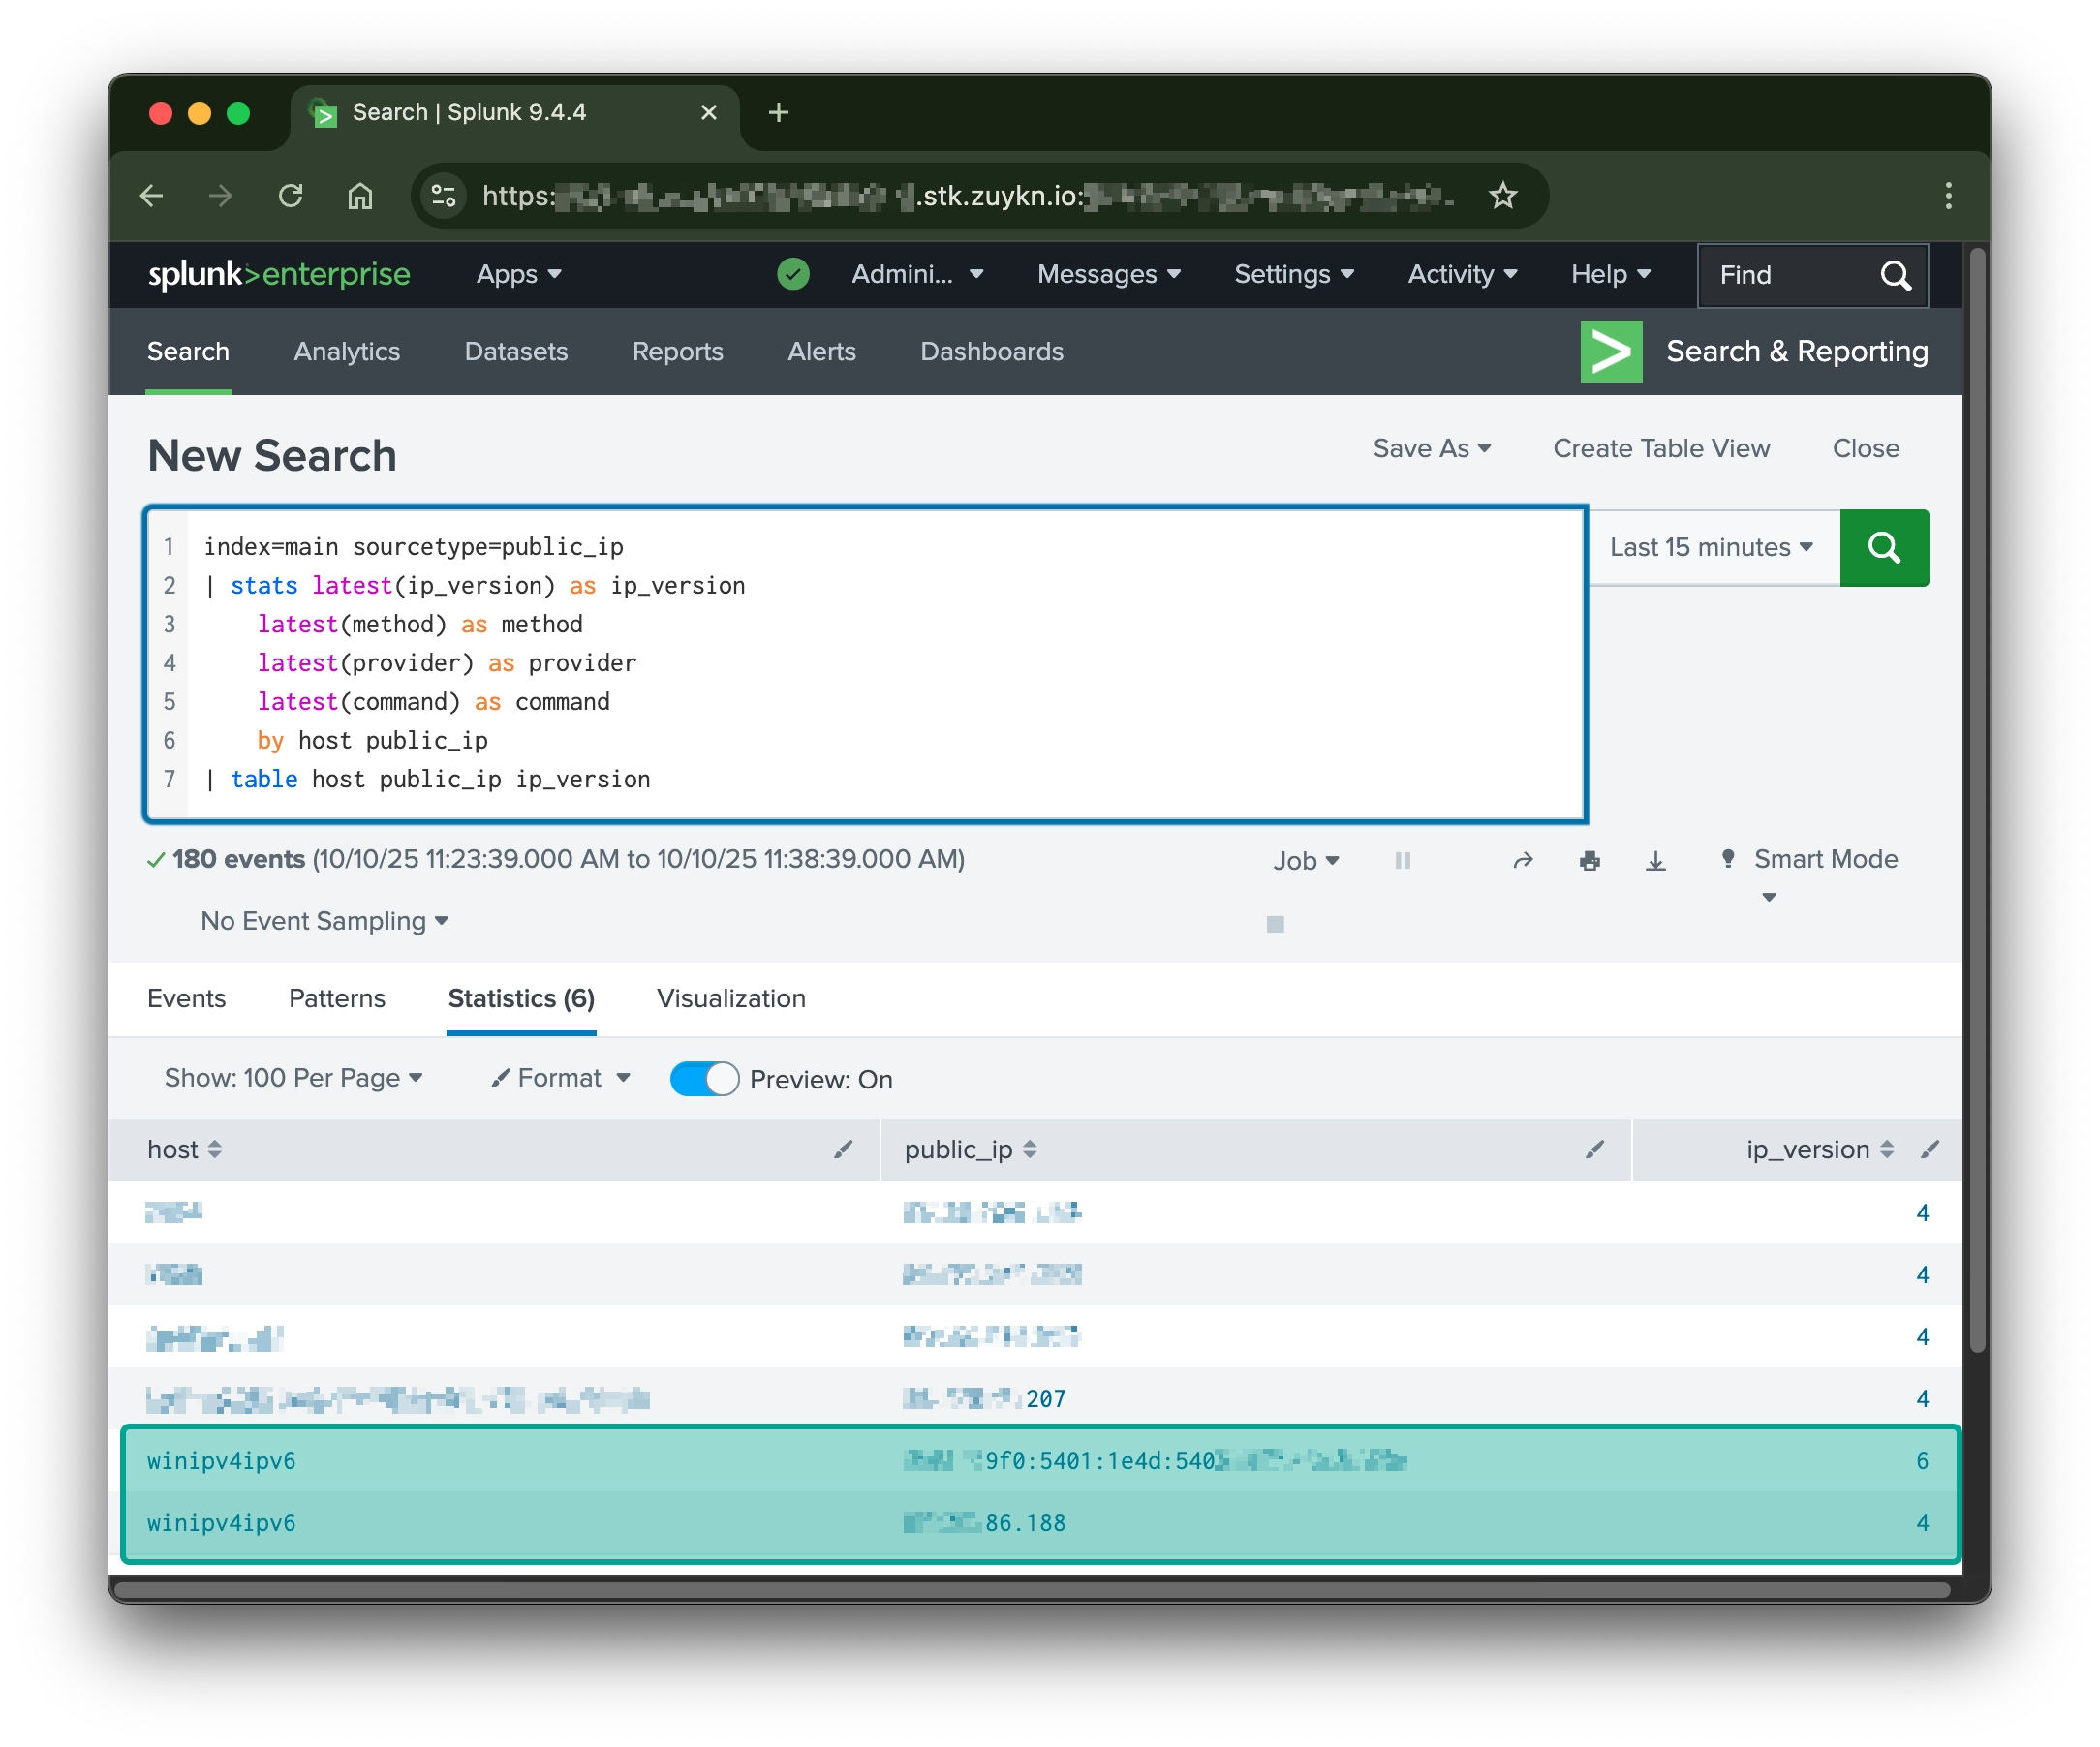
IPv4 and IPv6, Every Host
Dual-stack collection on Universal Forwarders and full Splunk instances.
Nothing to Install
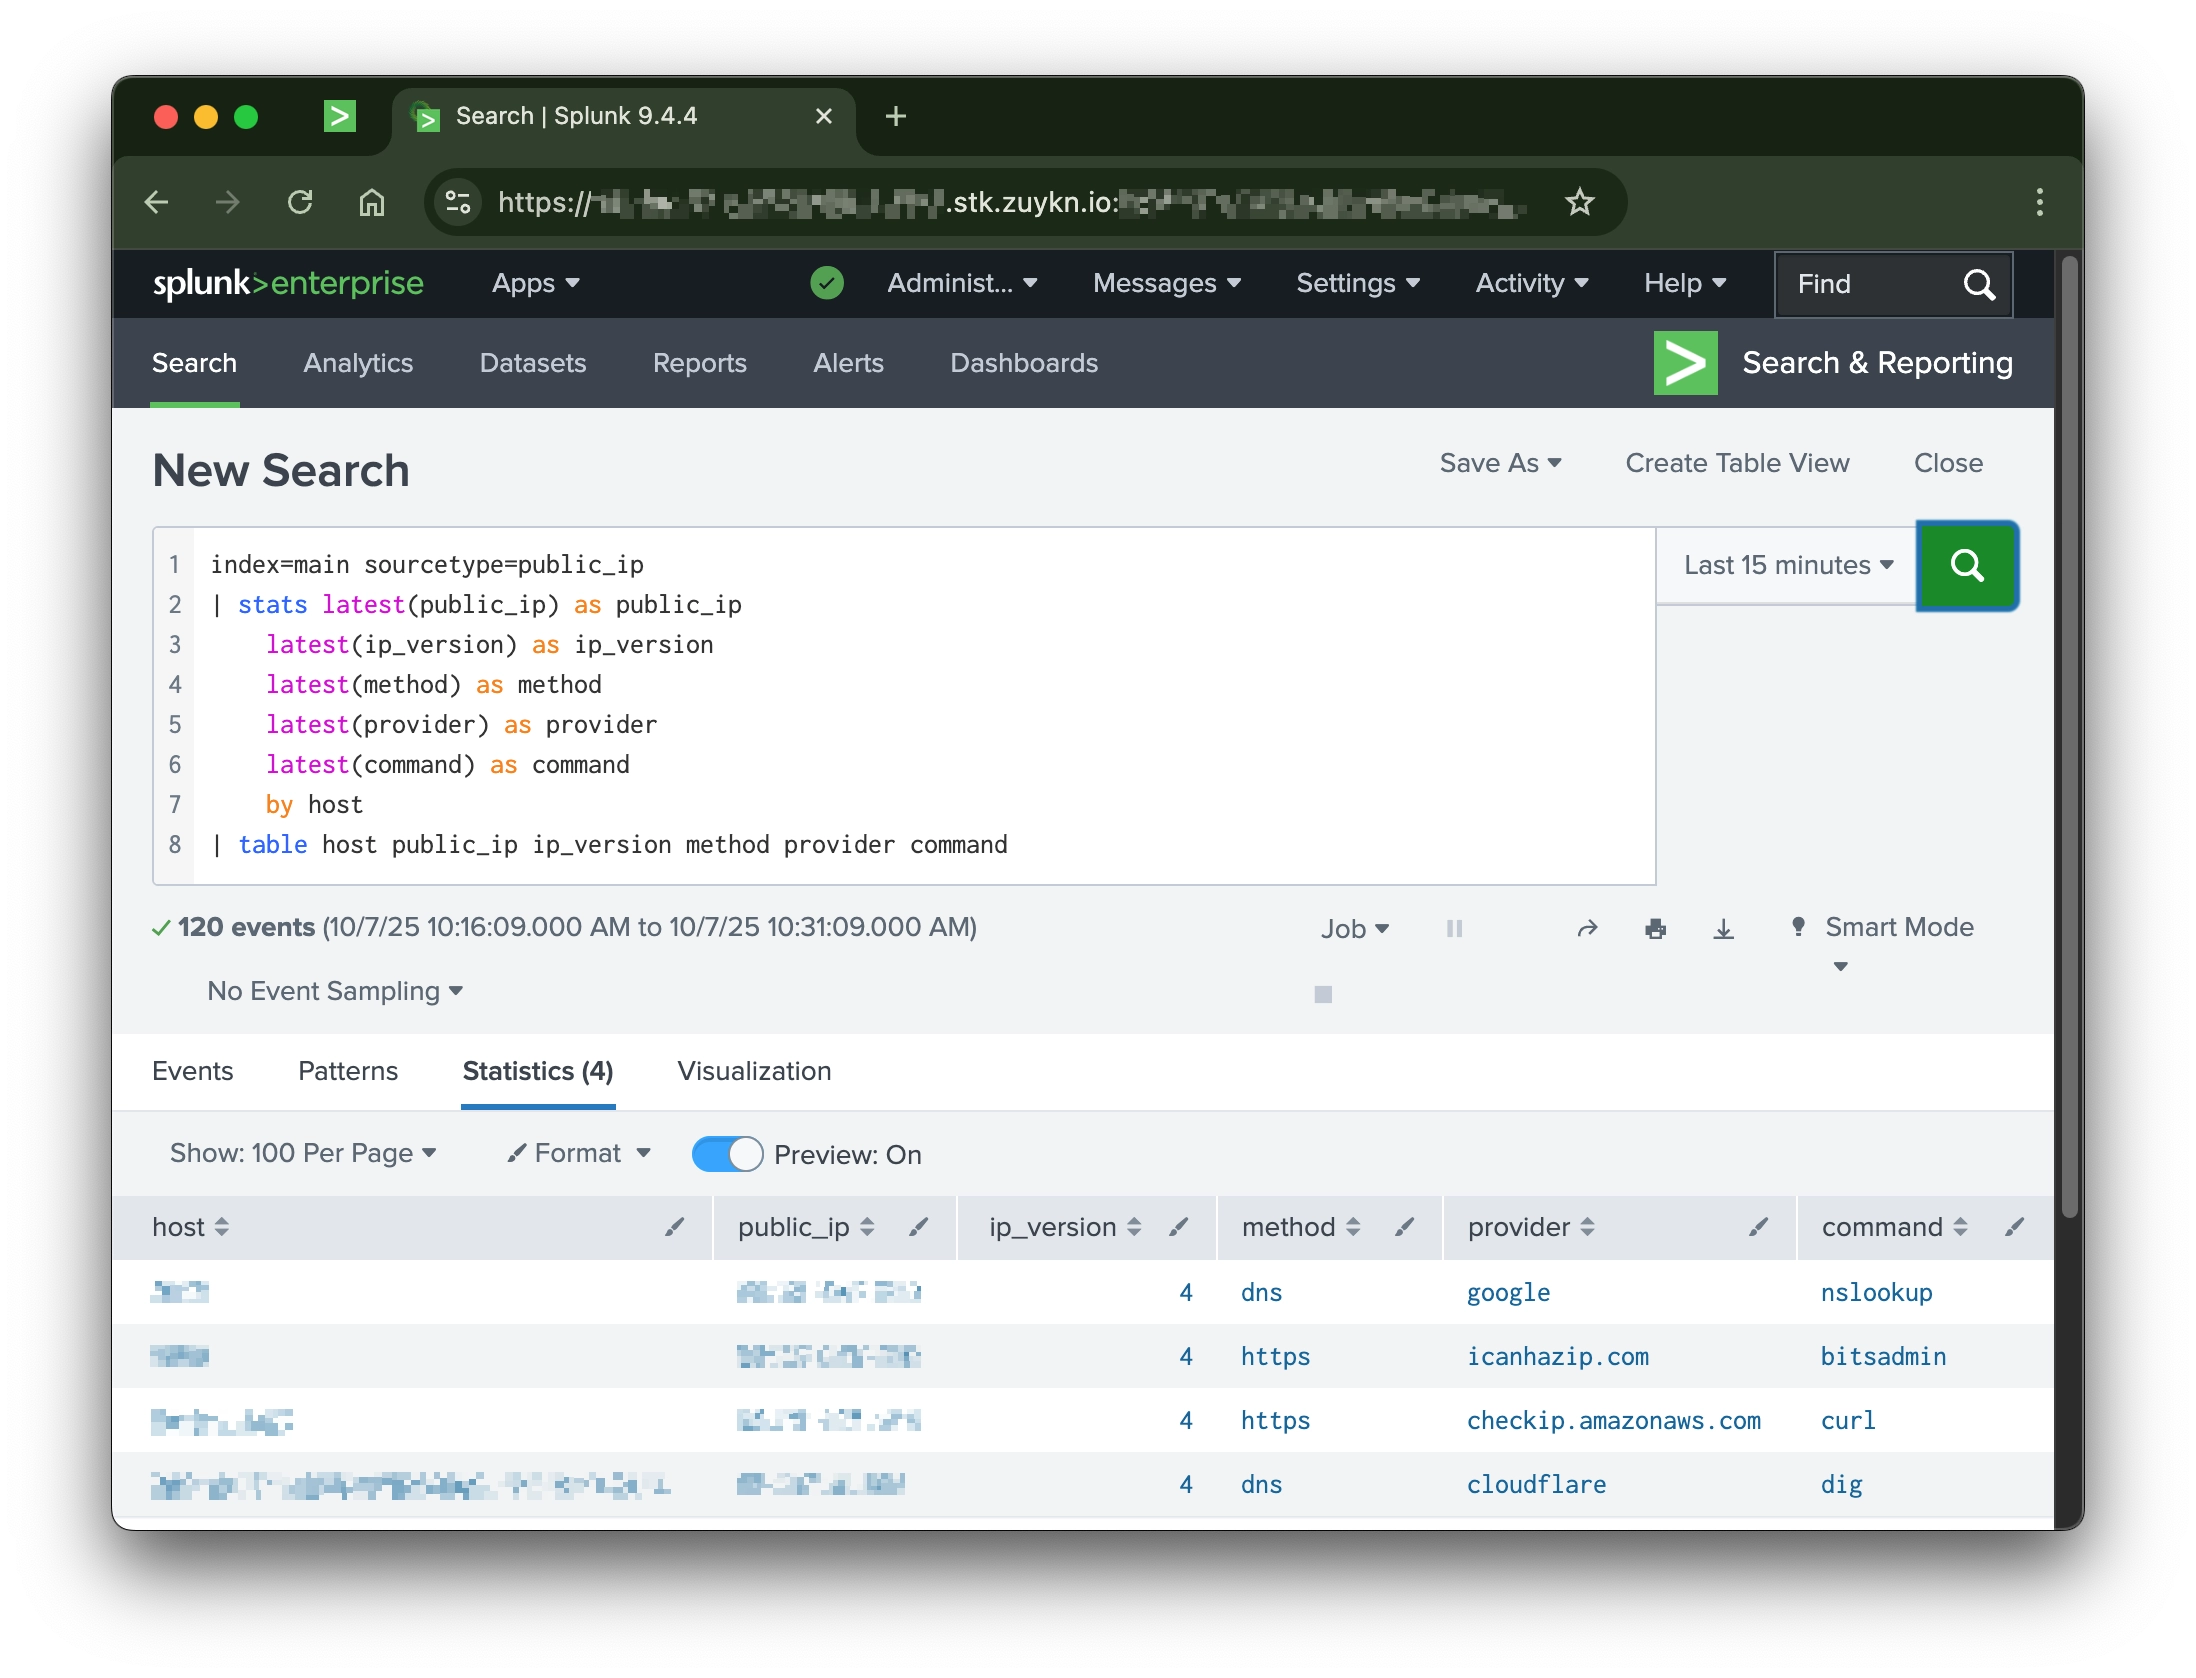
Uses tools already on the host, such as curl, dig and nslookup.
One Event per Run
Host, public IP, IP version, method and provider, over HTTPS or DNS with automatic fallback.
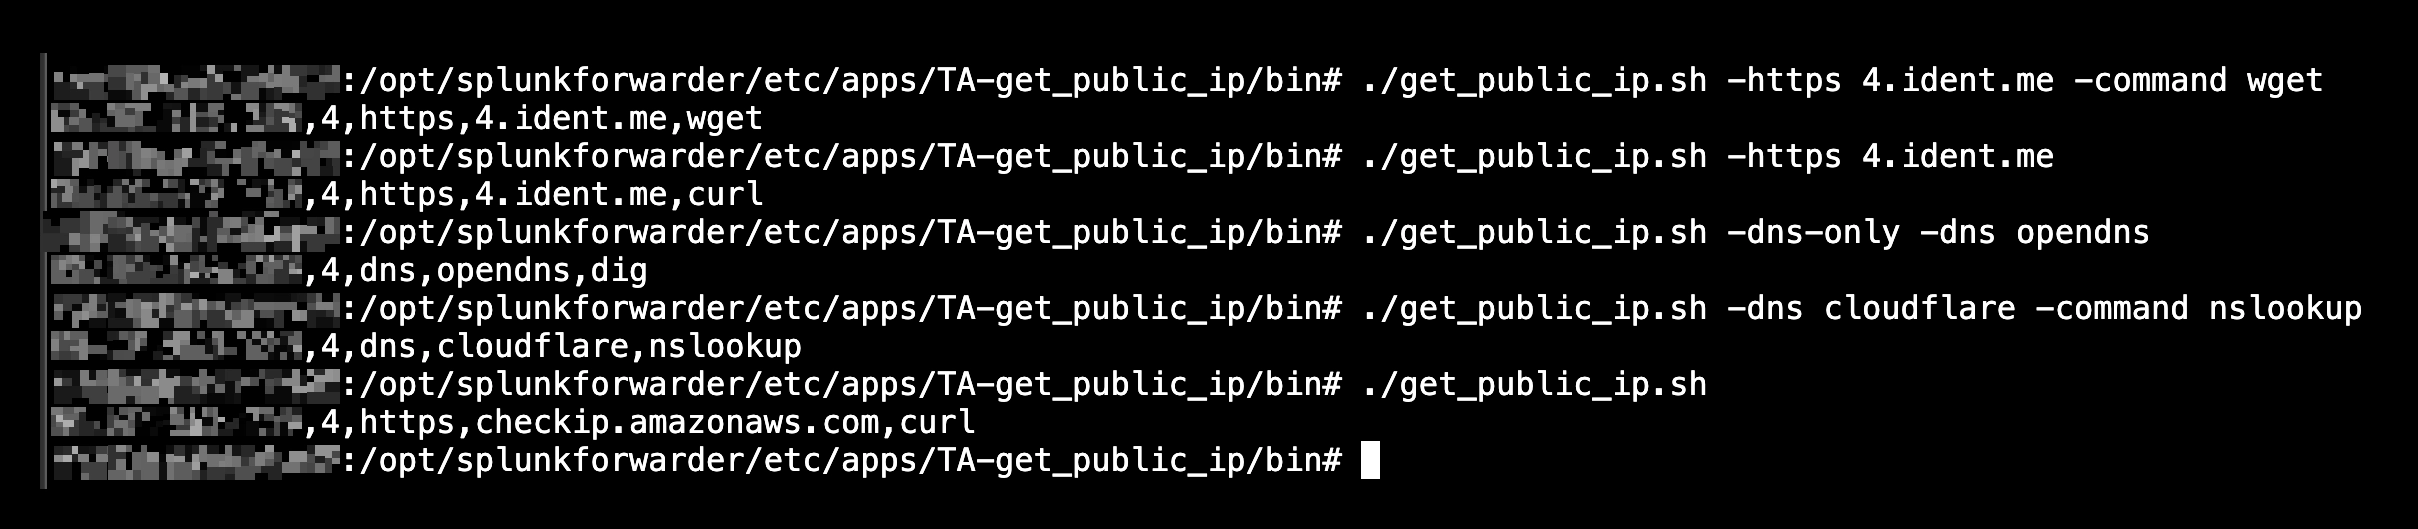
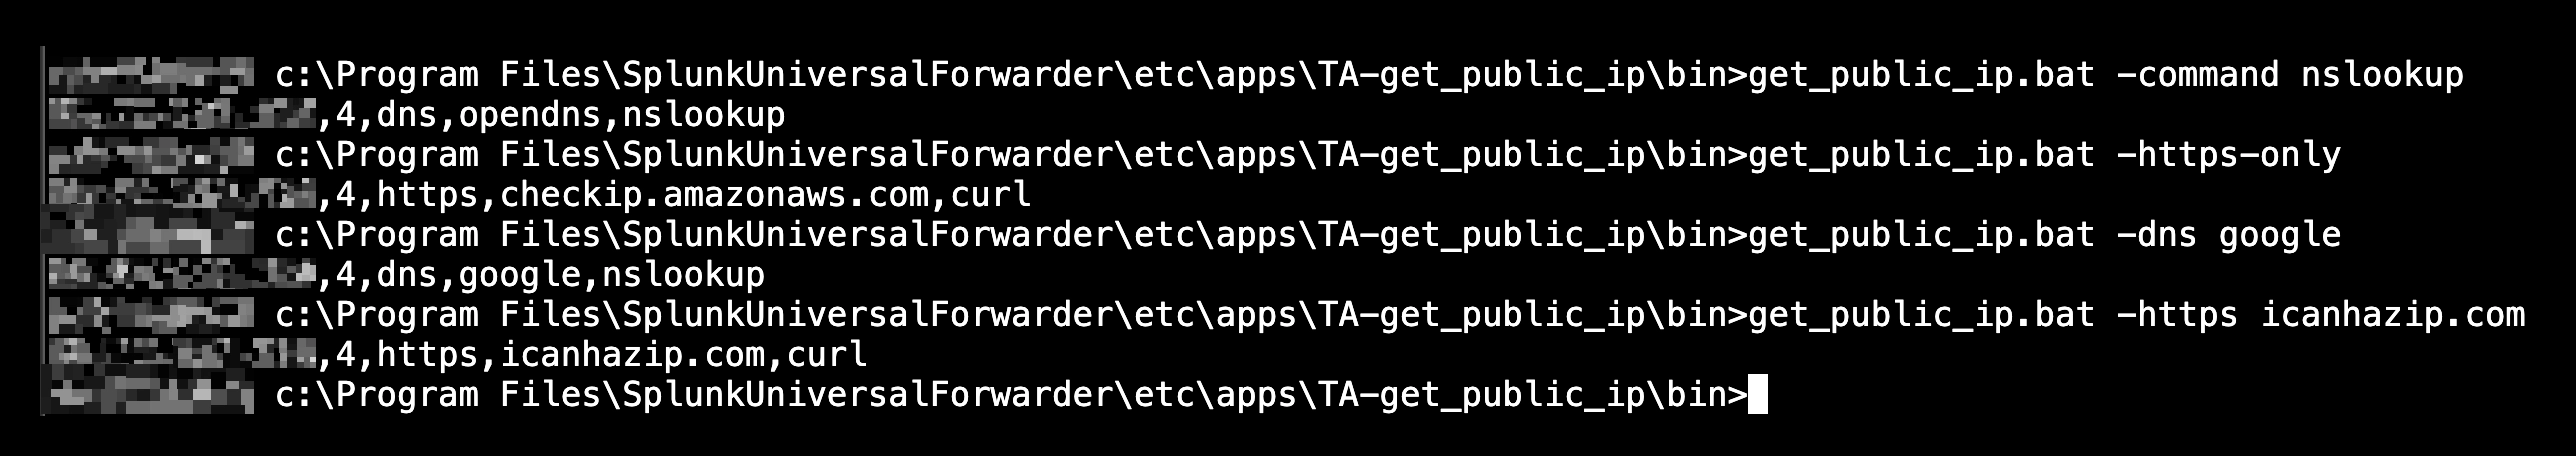
Overview
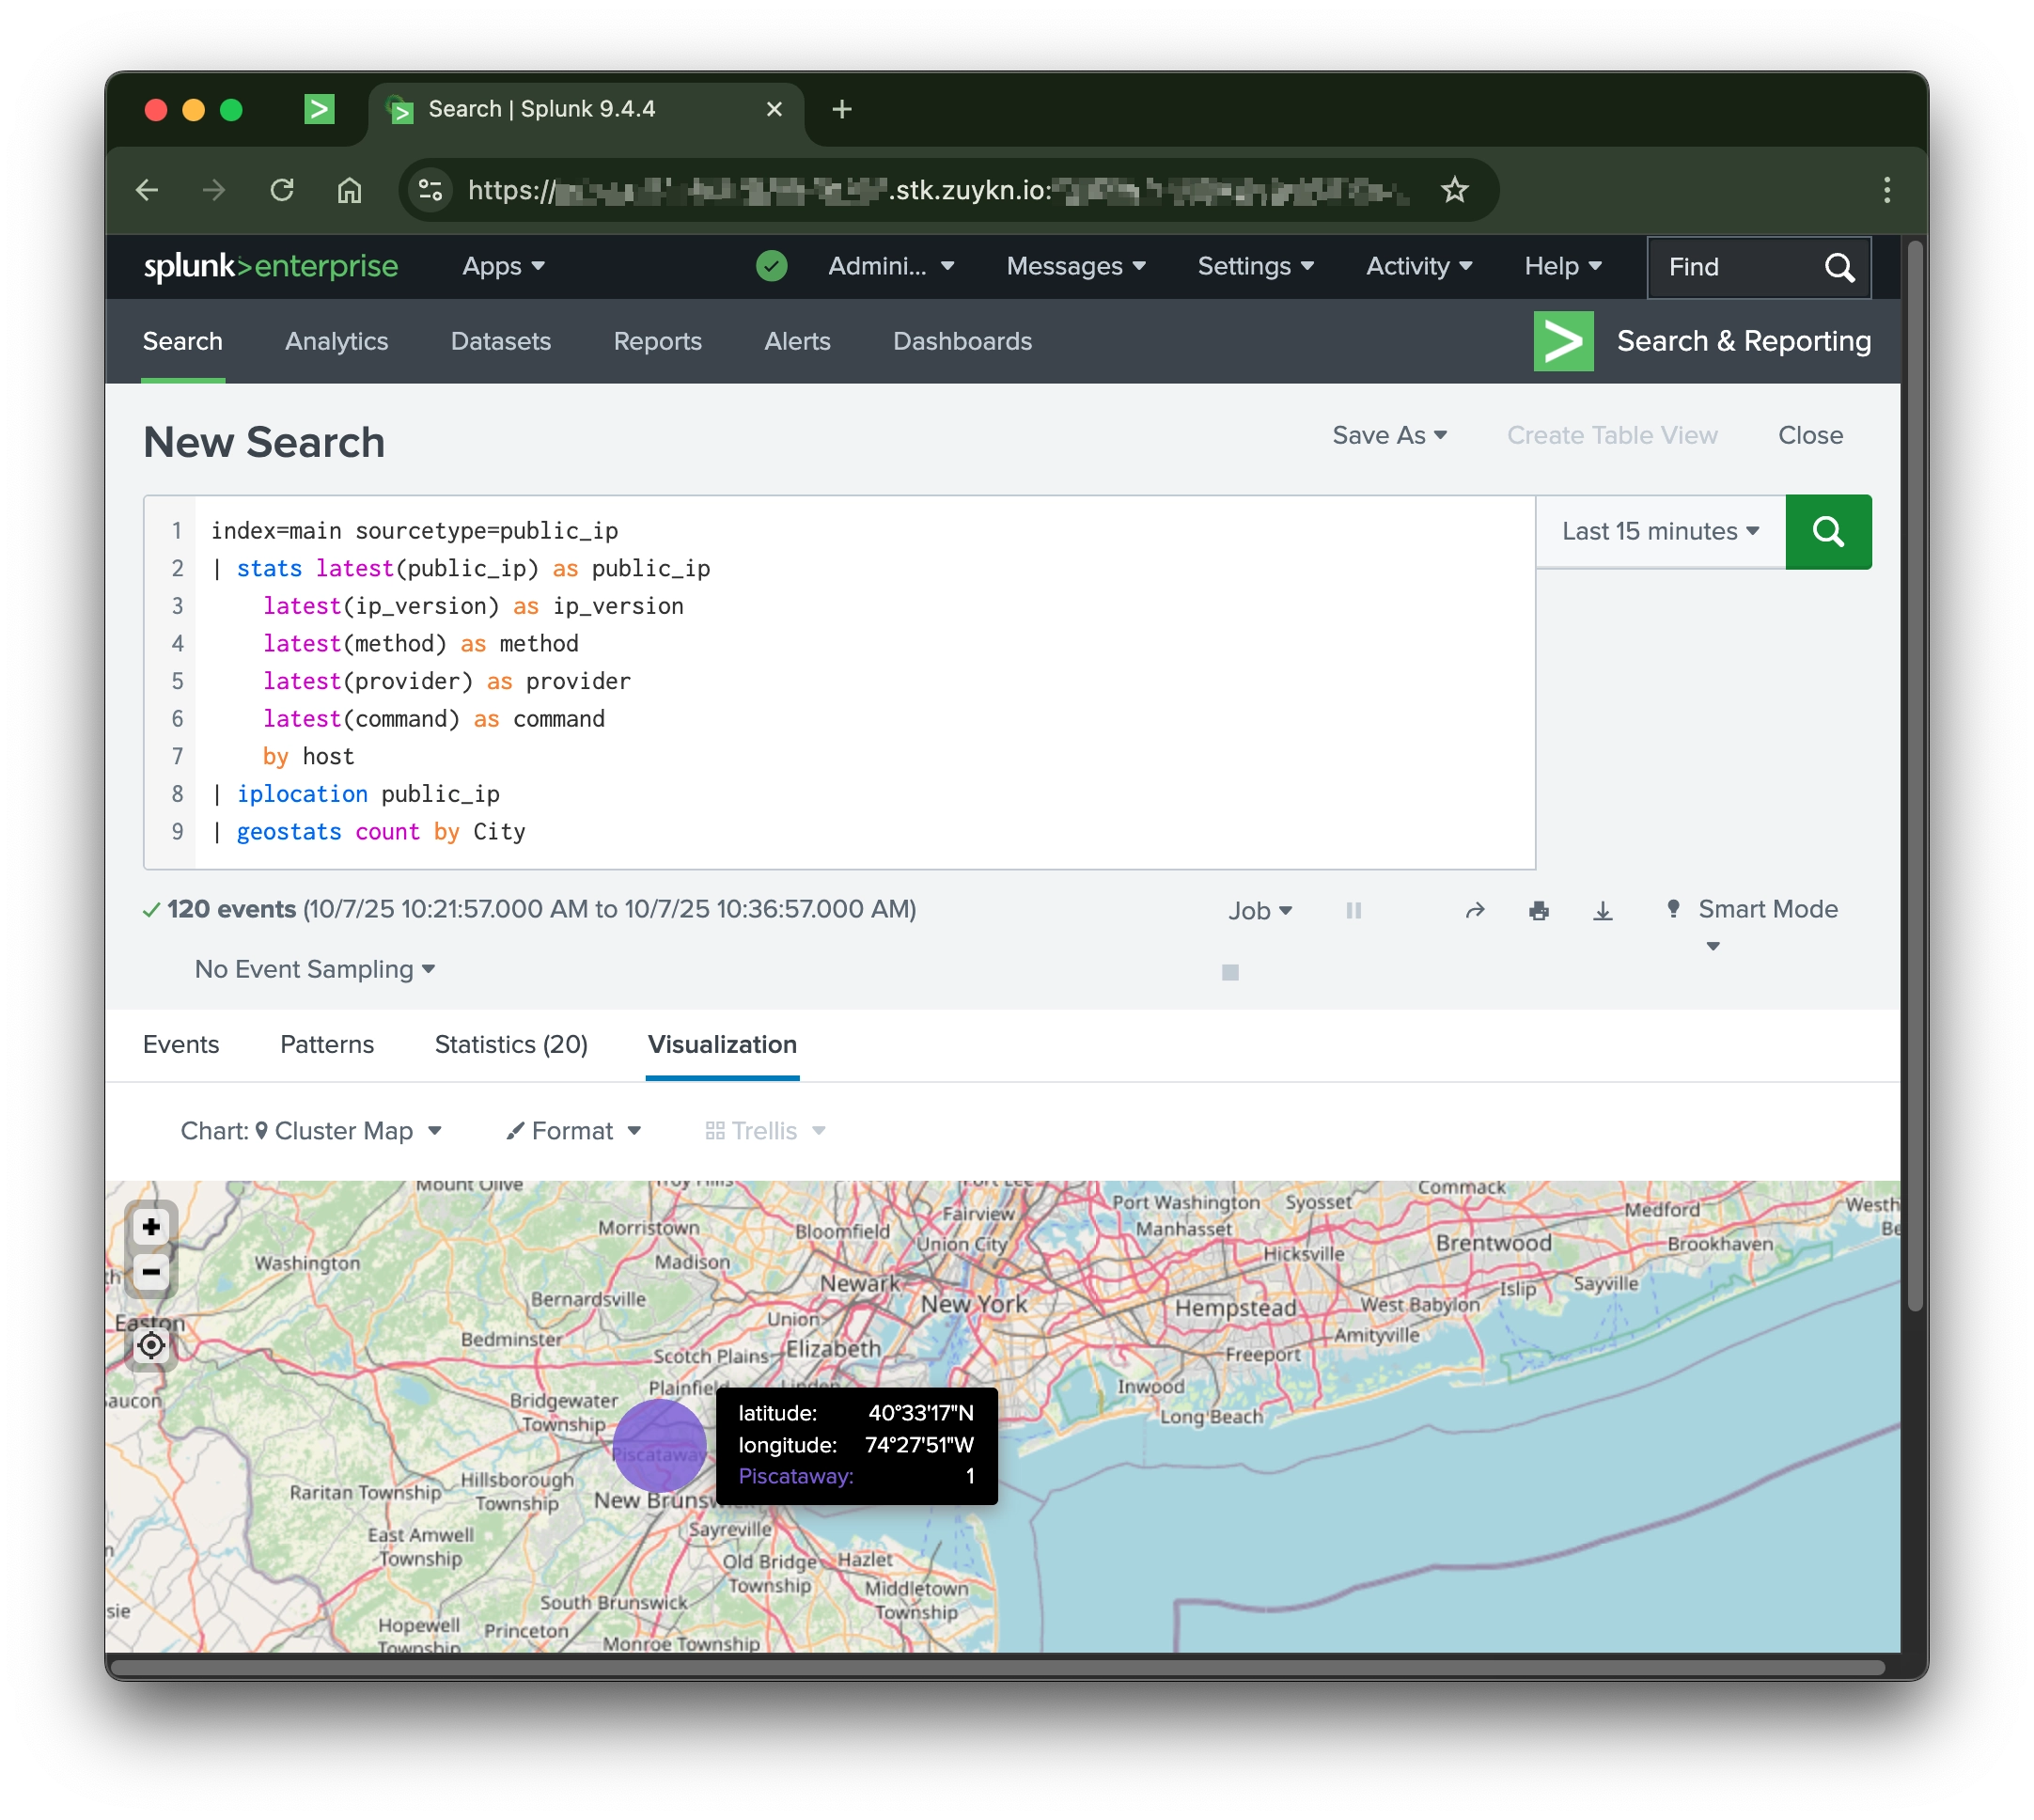
Know which public IP each Splunk host uses to reach the internet. The add-on collects it on a schedule, using only tools already on the host, and sends it to Splunk as a searchable event.
Features
- Public IPv4 and IPv6 (dual-stack) collection
- Windows, macOS, Linux and Unix, on Universal Forwarders and full Splunk instances
- HTTPS endpoint or DNS resolver lookup, with automatic fallback
- Built-in tools only, with a low chance of tripping EDR
- Negligible CPU and memory use
Use Cases
- Map which public IPs your forwarders use, by host and location
- Spot hosts whose public IP changes, or that leave through an unexpected network
- Correlate firewall and perimeter logs with the hosts behind them
Get Started
- Download the add-on from Splunkbase.
- Install it on Universal Forwarders for collection, and on search heads for field extractions.
- Set the index and interval in inputs.conf (default 300 seconds) and enable the scripted input.
- Restart the forwarder, then search sourcetype=public_ip.
Need a Tool That Doesn’t Exist Yet?
We build Splunk apps, Outlook add-ins and internal tools like this one for clients.
Have One Built →